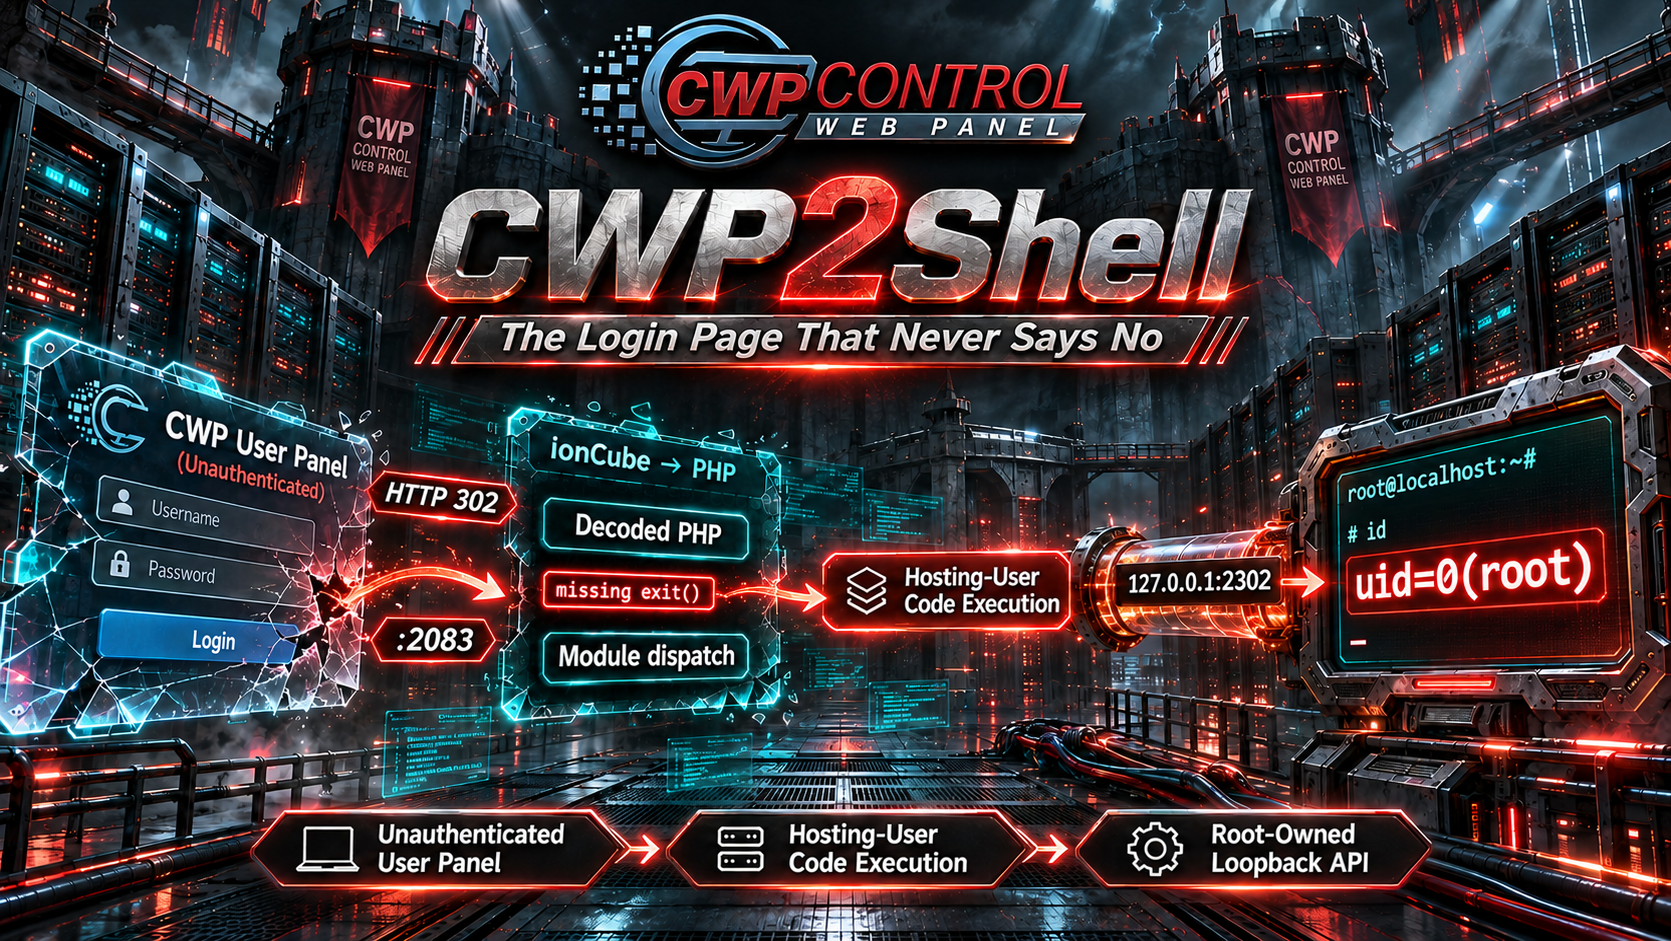
CWP2Shell: The Login Page That Never Says No
VulnCheck's Initial Access Intelligence team details an unauthenticated pre-auth remote root RCE chain in Control Web Panel, where the user panel emits its login redirect without stopping execution, so an attacker-named module file runs before authentication and a root-owned user API turns that foothold into uid 0.
FileRun: Four More Ways to Run Your Files
Four authenticated RCEs in FileRun. A contact-sheet handler and a settings test endpoint run attacker input through a shell, and a delegated administrator turns a control-panel field into stacked SQL that a permission-blob deserialization weaponizes into a webshell. All fixed in 2026.3.0.
Windfall: From Path Traversal to RCE in Nextcloud Flow & Windmill
Critical vulnerabilities in Windmill: unauthenticated path traversal leading to RCE, plus an authenticated SQL injection enabling full privilege escalation (operator → super admin → root RCE). Affects standalone Windmill and Nextcloud Flow.
CVE-2026-27743 through CVE-2026-27747: Five Vulnerabilities in SPIP Plugins
Five vulnerabilities across SPIP plugins: two SQL injections, two RCE (one unauth, one auth), and reflected XSS. Same template engine, same mistakes, different entry points.