ʞʞıdɐɔoɥƆ
Security Researcher & Exploit Developer
at VulnCheck
Breaking, building, and documenting. Vulnerability research, exploit development, and offensive security.
✦ Latest
Code of the Day: Unauthenticated Root in Copeland XWEB EVO
VulnCheck's Initial Access Intelligence team discloses 14 vulnerabilities in the Dixell / Copeland XWEB EVO refrigeration supervisor, including unauthenticated remote root on both the legacy builds and the current end-of-support firmware, where the login handler runs the submitted username as a shell command before the password check, the interpreter behind every page is setuid root, and the daily admin credential is a secret-free function of the device MAC and the date.
Read articleRecent
all →One Recovery Code, Two Shells in Control Web Panel
VulnCheck's Initial Access Intelligence team discloses two vulnerabilities in Control Web Panel that both end in code execution as the hosting account from the same primitive, an account password-recovery code. One poisons the reset link's Host header to leak the code, and the other feeds that code to the administration API, which accepts it as OAuth authorization.
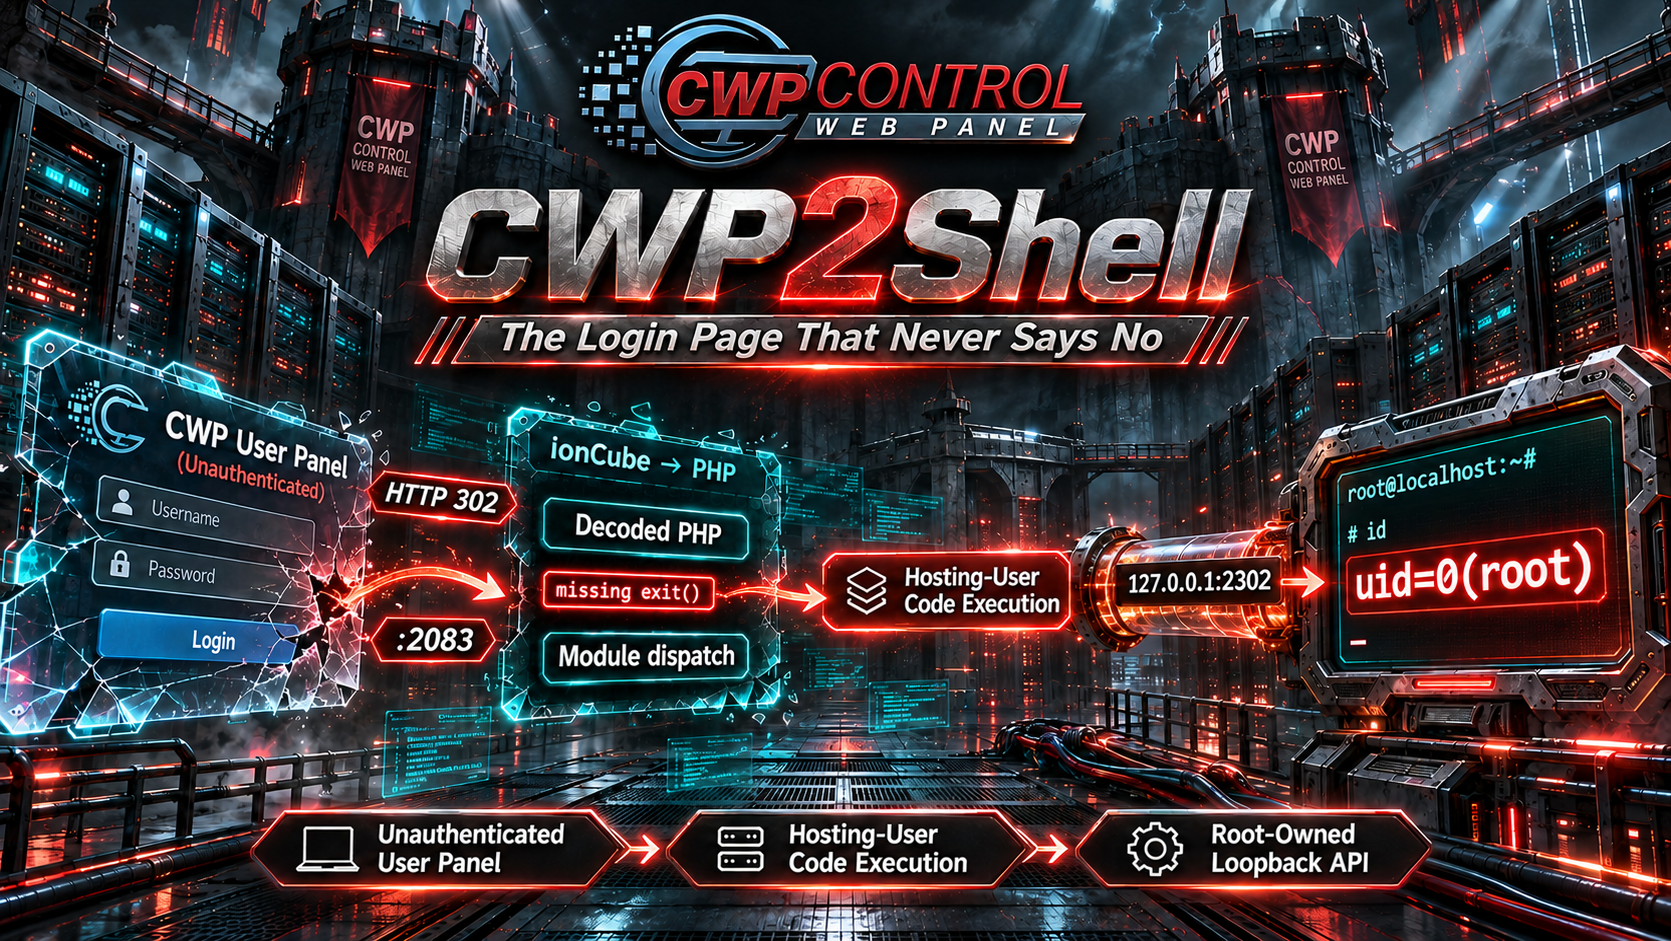
CWP2Shell: The Login Page That Never Says No
VulnCheck's Initial Access Intelligence team details an unauthenticated pre-auth remote root RCE chain in Control Web Panel, where the user panel emits its login redirect without stopping execution, so an attacker-named module file runs before authentication and a root-owned user API turns that foothold into uid 0.
SPIP odt2spip Plugin: Authenticated Command Injection via Uploaded Document Filename
VulnCheck's Initial Access Intelligence team details an authenticated OS command injection in the SPIP odt2spip plugin, where an uploaded document's filename is concatenated into a shell command and run, giving any low-privileged author remote code execution as the web server user.
Xorbits Xoscar: Unauthenticated RCE via Cloudpickle Deserialization in the Actor Pool
VulnCheck's Initial Access Intelligence team details an unauthenticated remote code execution in Xoscar, the actor and RPC framework behind the Xinference inference stack, where the actor pool deserializes every inbound TCP message with cloudpickle before it checks the message type and with no authentication.
JCTables for Joomla: When "Already Escaped" Means Injectable
VulnCheck's Initial Access Intelligence team details an unauthenticated JSON CRUD API in the JCTables component for Joomla whose escape helper trusts any value already wrapped in single quotes, turning one URL into arbitrary SQL read and write and, through a borrowed admin session, into remote code execution.
Virtualizor: The Login Parameter That Skips the Login
VulnCheck's Initial Access Intelligence team details an unauthenticated remote root RCE in the Virtualizor admin panel, where the pre-auth billing-module hook is guarded only against requests whose act is not 'login', so act=login walks straight into it, the hook unserializes an attacker POST field and splices its uid into a root shell, and the parameterized queries do not help because MySQL casts the injected string back to the integer the query expects.
NEVER GONNA
GIVE YOU UP
You were warned.