Virtualizor: The Login Parameter That Skips the Login
VulnCheck's Initial Access Intelligence team details an unauthenticated remote root RCE in the Virtualizor admin panel, where the pre-auth billing-module hook is guarded only against requests whose act is not 'login', so act=login walks straight into it, the hook unserializes an attacker POST field and splices its uid into a root shell, and the parameterized queries do not help because MySQL casts the injected string back to the integer the query expects.
FileRun: When Your File Manager Runs Your Files
OS Command Injection in FileRun's thumbnail generation - authenticated (CVSS v4 8.7) or via public 'file request' weblinks (CVSS v4 9.2). The extractors wrap file paths in double quotes and pass them to exec(), but the filename sanitizer allows $(){}` - enough for command substitution. The weblink path uploads a malicious filename via anonymous upload, then self-triggers thumbnail generation through the public listing.

Aimy Captcha-Less Form Guard: The Anti-Bot Plugin That Hands Bots the Keys
An unauthenticated PHP object injection in Aimy Captcha-Less Form Guard for Joomla, where a repeating-key XOR published alongside its own ciphertext turns every protected form into an unserialize() sink and, on Joomla 3.9 through 5.2.1, into remote code execution.
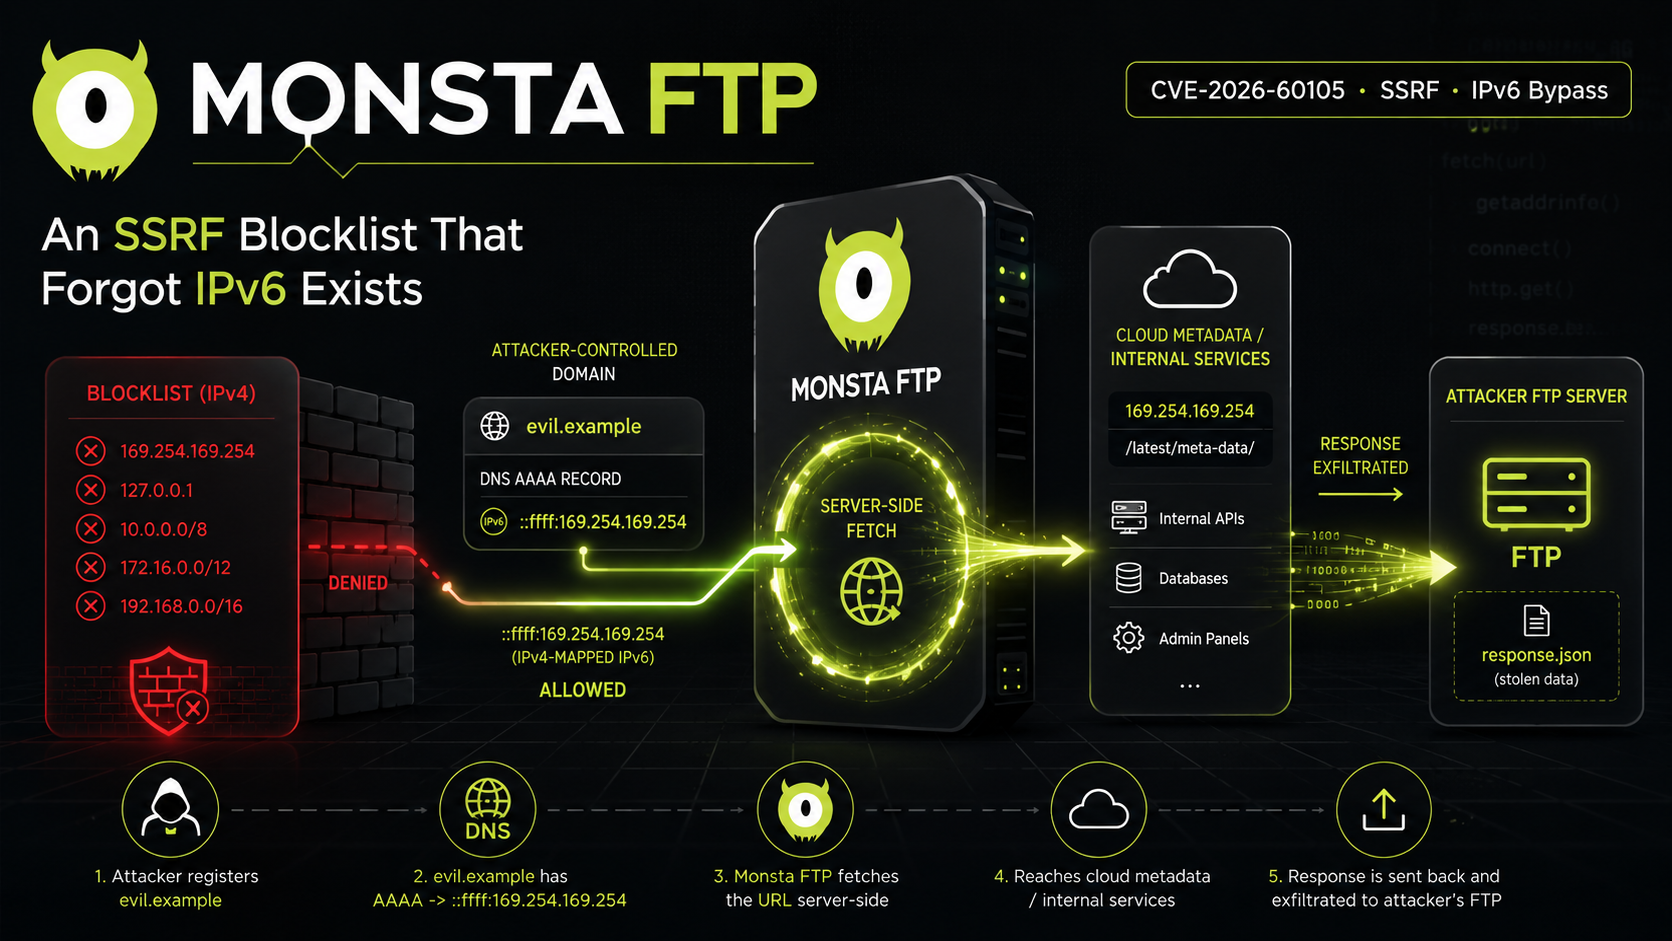
Monsta FTP: An SSRF Blocklist That Forgot IPv6 Exists
An unauthenticated SSRF in Monsta FTP 2.14.4. The product ships a real SSRF blocklist that correctly blocks 127.0.0.1, 169.254.169.254 and RFC1918, then forgets that ::ffff:169.254.169.254 is the exact same host. One missing normalization, both gates bypassed, and a static AAAA record is all it takes.