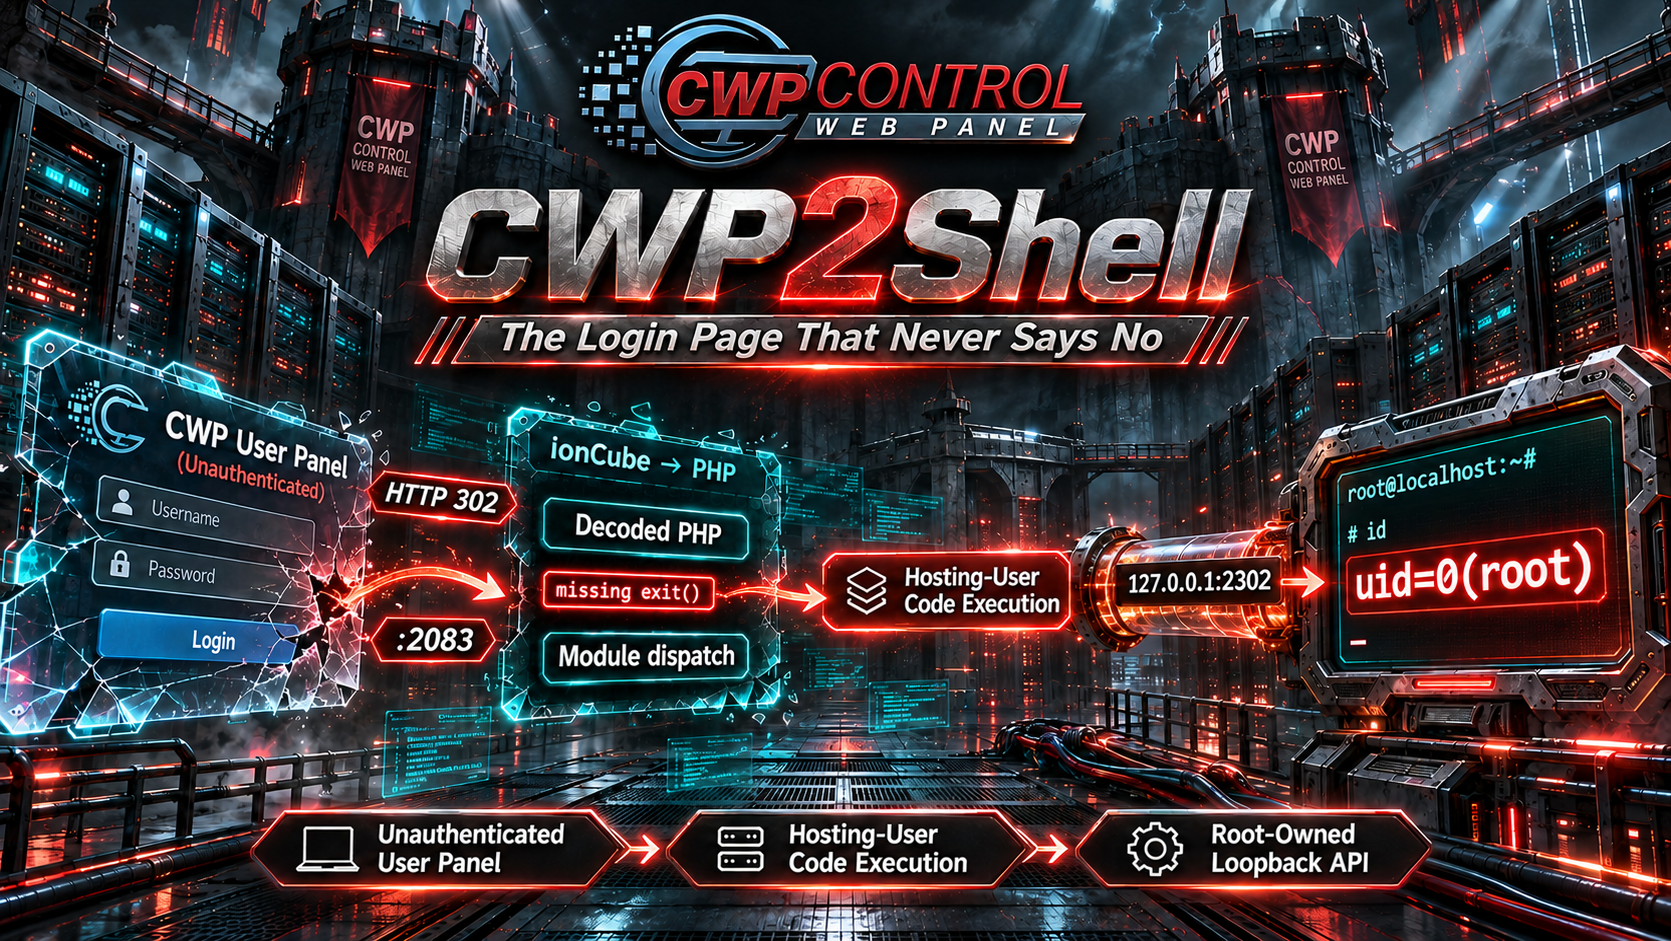
CWP2Shell: The Login Page That Never Says No
VulnCheck's Initial Access Intelligence team details an unauthenticated pre-auth remote root RCE chain in Control Web Panel, where the user panel emits its login redirect without stopping execution, so an attacker-named module file runs before authentication and a root-owned user API turns that foothold into uid 0.
CVERCEPHP