Xorbits Xoscar: Unauthenticated RCE via Cloudpickle Deserialization in the Actor Pool
VulnCheck's Initial Access Intelligence team details an unauthenticated remote code execution in Xoscar, the actor and RPC framework behind the Xinference inference stack, where the actor pool deserializes every inbound TCP message with cloudpickle before it checks the message type and with no authentication.
Virtualizor: The Login Parameter That Skips the Login
VulnCheck's Initial Access Intelligence team details an unauthenticated remote root RCE in the Virtualizor admin panel, where the pre-auth billing-module hook is guarded only against requests whose act is not 'login', so act=login walks straight into it, the hook unserializes an attacker POST field and splices its uid into a root shell, and the parameterized queries do not help because MySQL casts the injected string back to the integer the query expects.
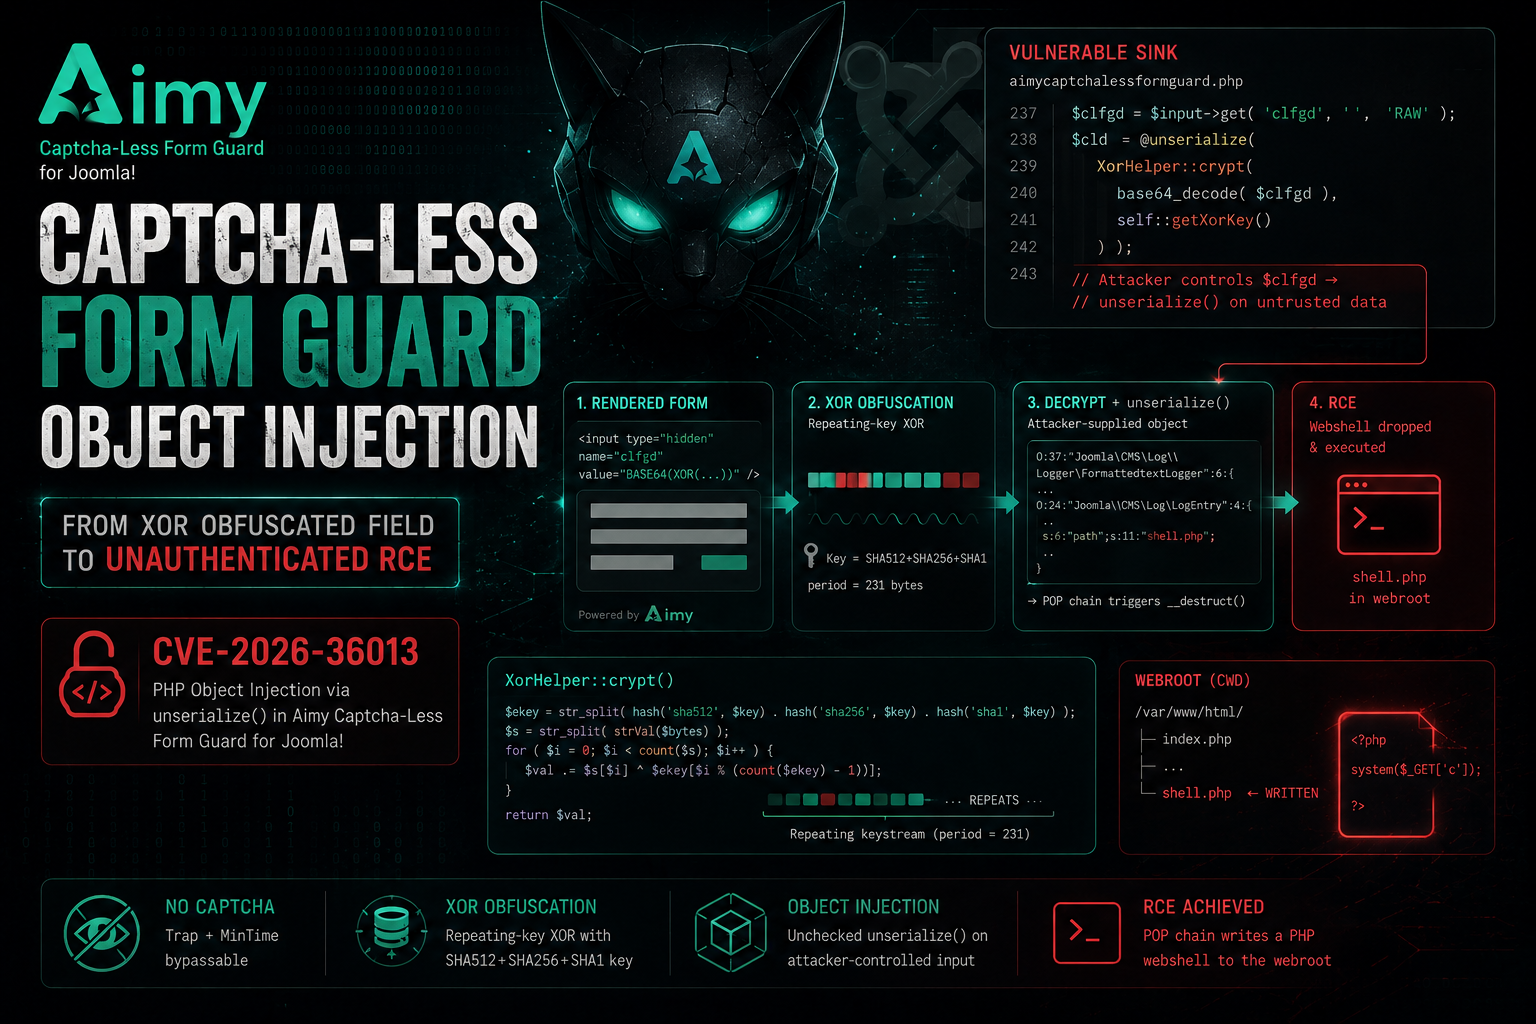
Aimy Captcha-Less Form Guard: The Anti-Bot Plugin That Hands Bots the Keys
An unauthenticated PHP object injection in Aimy Captcha-Less Form Guard for Joomla, where a repeating-key XOR published alongside its own ciphertext turns every protected form into an unserialize() sink and, on Joomla 3.9 through 5.2.1, into remote code execution.